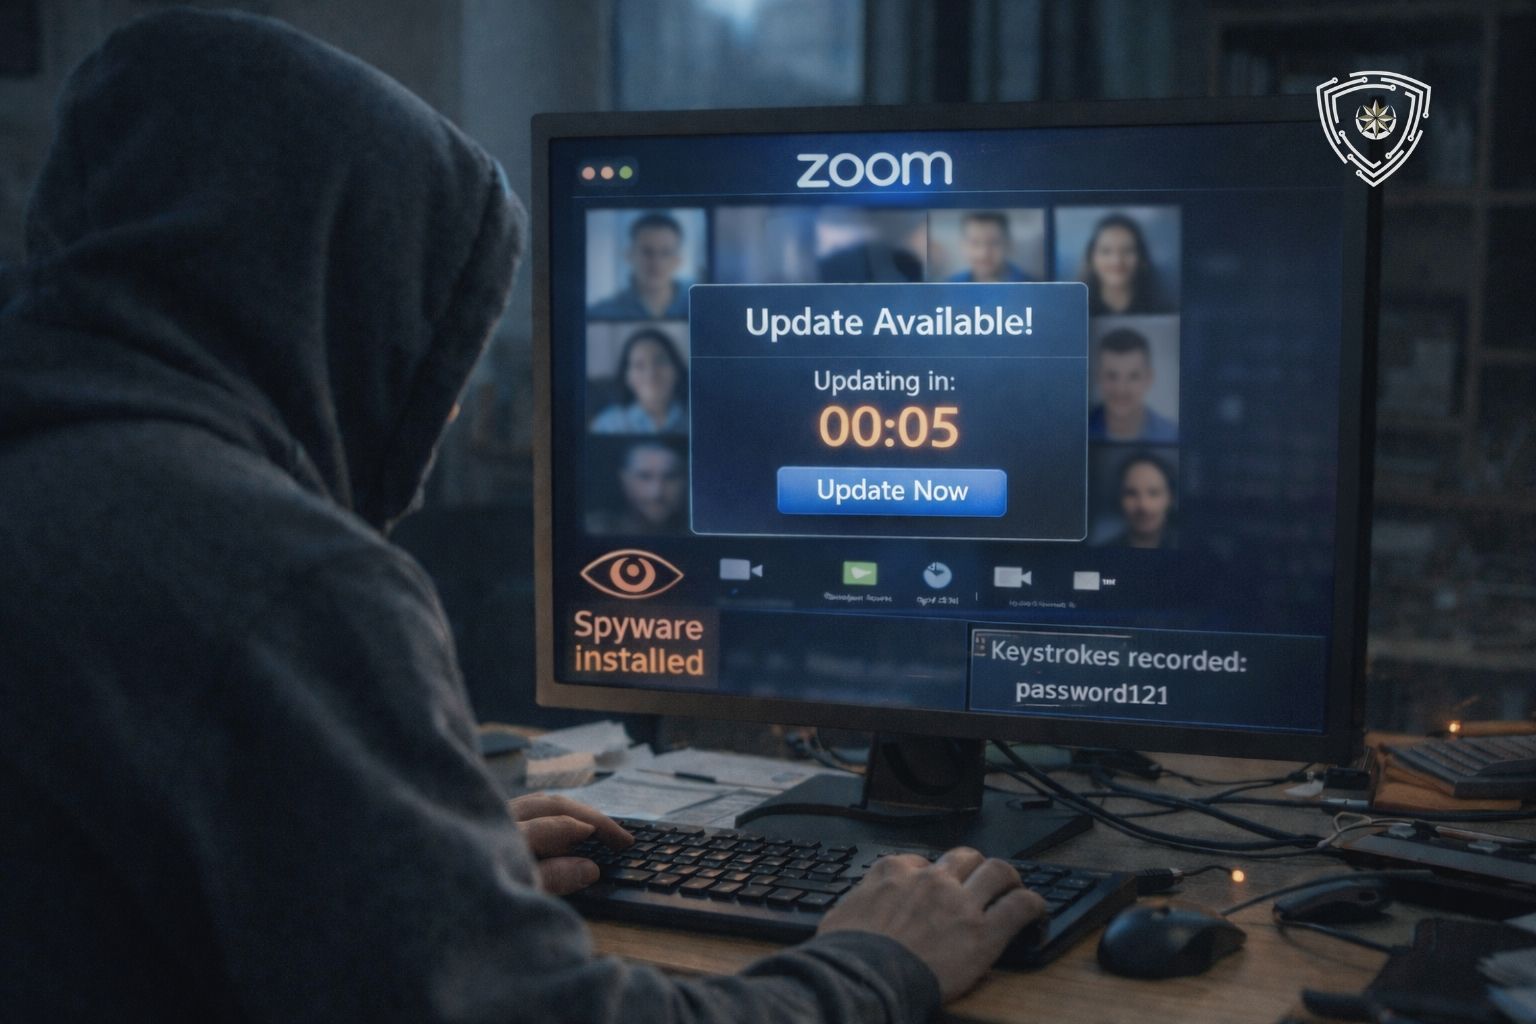
Researchers have warned of a new fake Zoom meeting campaign targeting Windows users. According to the reports, the attack chain deceives employees into visiting a convincing imitation of a Zoom video-call page. Shortly after the victim opens the link, an automatic “Update Available” prompt and countdown appear, and a malicious installer is downloaded and executed without explicit user consent. The technique is assessed as a more convincing variant of clickjacking.
According to the analysis, the software installed is a covert build of Teramind, a commercial monitoring tool that organizations may use to track employee activity on work computers. However, in the hands of a threat actor, it effectively becomes a surveillance tool. Such software can log keystrokes, capture screenshots at regular intervals, record visited websites and opened applications, collect clipboard contents, and track email and file activity. Experts add that detection may be challenging because the tool can appear to be a legitimate application, causing some security solutions to treat it as benign.
Researchers note that Zoom is an attractive tool for attackers because it is widely used in workplace settings. Since employees are accustomed to receiving meeting invitations from managers, colleagues, and customers, they may click links without checking it carefully. In this campaign, victims are redirected to the impersonation domain uswebzoomus[.]com/zoom/. Taking a few seconds to verify that the link really goes to the official zoom.us domain can help to prevent serious risk. It is also emphasized that fake meeting invites can be delivered through both Gmail and Microsoft Outlook, and in some cases may even be automatically added to a user’s calendar. Analyses further indicate that subject lines designed to create urgency, such as “final notice” style prompts and invitations arriving at unusual times (e.g., on a Sunday) are common indicators that increase the likelihood of phishing.
Security experts say the first line of defense in cases like this is employee awareness training. Staff should be taught to treat unexpected invitations with caution, avoid joining meetings that list unfamiliar names or email addresses, and, most importantly, to double-check any request that asks them “install or update software to join a meeting” using a trusted method outside the message. Experts also emphasize that if a link leads to unusual behavior after it is clicked (for example, the page starts downloading a file), it should be treated as suspicious and reported to the organization’s security team as an incident. They add that phishing pages are becoming more real and more targeted with the help of AI, which further increases the risk.
 31 July 2026
 28 July 2026
 27 July 2026
 22 July 2026
 20 July 2026
 17 July 2026
 16 July 2026
 16 July 2026
© 2011-2026 All rights reserved